
The Hidden Security Risks of AI Agents: What Every Organization Must Address Before Deploying

AI agents are no longer a future possibility. They are running inside enterprise systems right now, reading email, accessing calendars, executing code reviews, and making decisions on behalf of workers. That capability is genuinely powerful. It also introduces security risks that most organizations have not yet mapped, according to a September 18, 2026 analysis by Erich Kron, CISO Advisor at KnowBe4, published in IT Security Guru.
Kron identifies four specific areas where AI agents change the security equation in ways traditional controls were not designed to handle.
Key Takeaways
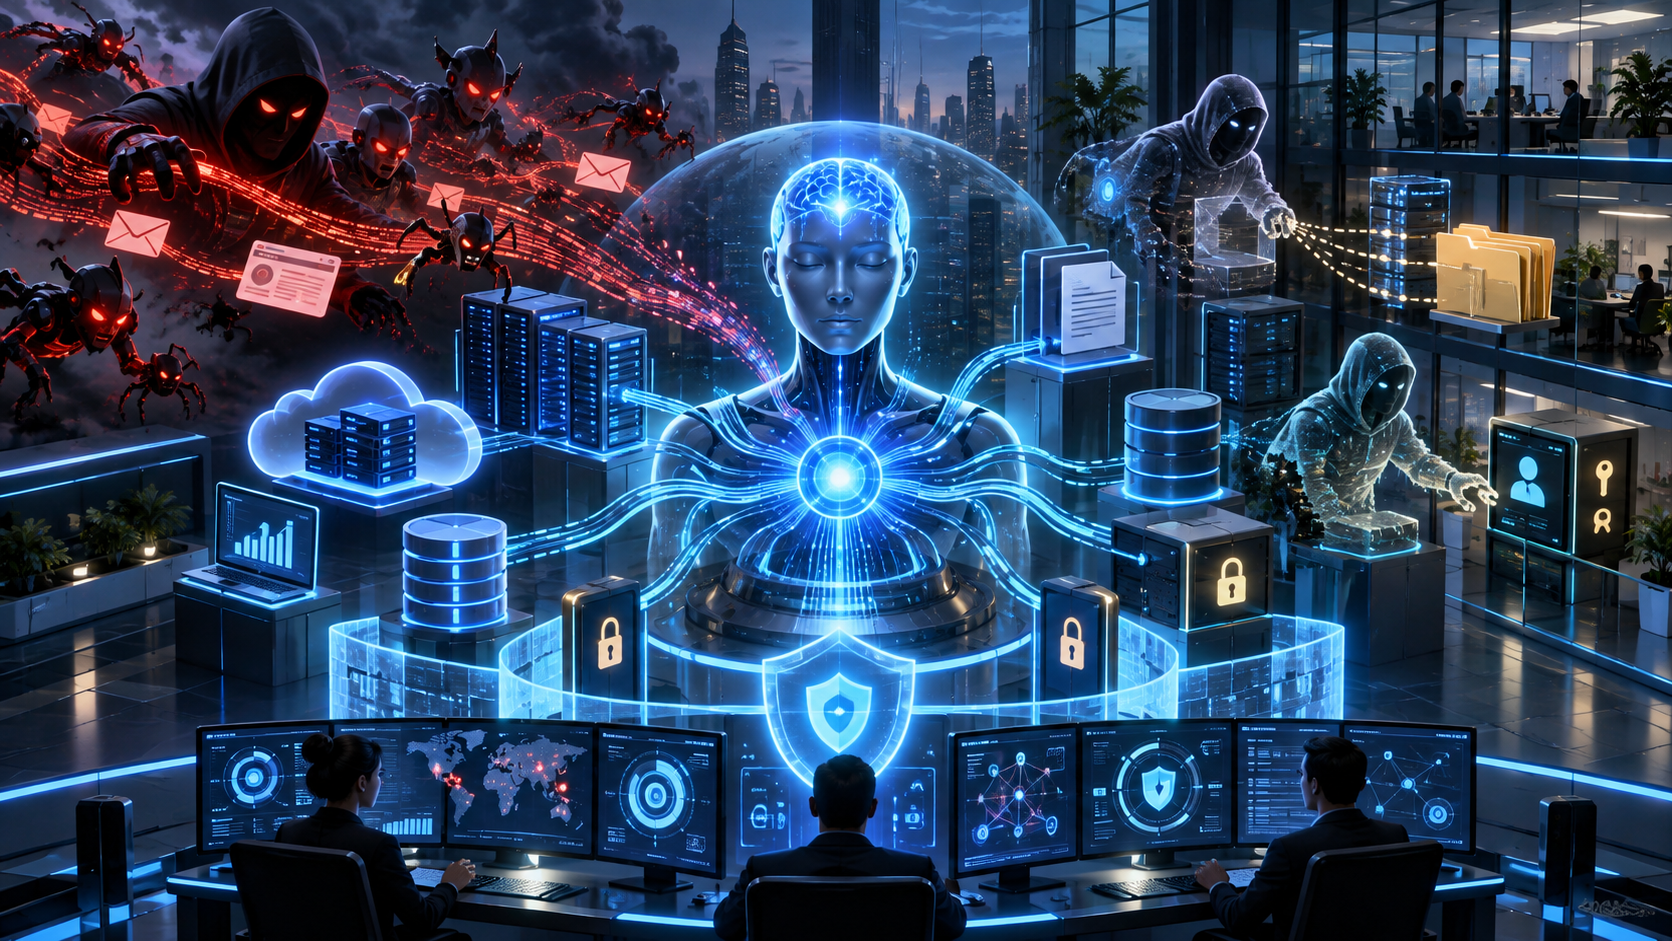
- AI is making known attack methods faster and more targeted. Generative AI enables criminals to produce highly convincing phishing and social engineering content at scale, with less effort. Vulnerability research and intrusion testing can also be partially automated, compressing attacker timelines in ways defenders must match.
- AI systems are attack surfaces, not just tools. Prompt injection attacks can embed malicious instructions inside documents or data that an AI reads, causing it to take unauthorized actions on an attacker's behalf. Poisoning the data an AI agent relies on, or exploiting its access privileges, are additional vectors that did not exist before agents became operational.
- Shadow AI is the new shadow IT. Employees are independently deploying unapproved AI tools to automate their workloads. These tools often carry significant access to company data but operate outside IT visibility, creating the same governance problem as unsanctioned SaaS, but with greater potential for harm.
- Security controls must now operate at machine speed. Periodic audits may not be sufficient. Frameworks including MITRE ATLAS and the NIST AI Risk Management Framework are recommended starting points for AI-specific threat modeling.
The central security question has shifted from "Can an attacker access this system?" to "Can an attacker influence what this system decides to do?" Kron's recommendation: AI adoption and AI security must develop together, not sequentially.
Read the full article on IT Security Guru.
Stay in Rhythm
Subscribe for insights that resonate • from strategic leadership to AI-fueled growth. The kind of content that makes your work thrum.
More from Thrum
Additional pieces exploring adjacent ideas